Rapid7 and Osto both help teams reduce cyber risk, but they approach the problem from different directions. Rapid7 has a broad security operations portfolio spanning exposure and vulnerability management, SIEM, cloud and application security, threat intelligence, MDR and CyberGRC. Osto is built as a one-stop cyber platform for startups and growing teams, combining preventive security, compliance automation, VAPT, questionnaires and security support in one place.
Osto vs Rapid7: comparing an all-in-one cyber platform with a security operations platform
Rapid7 is a strong fit when exposure management, vulnerability prioritisation, SIEM, detection and response, cloud security or managed security operations are central requirements.
Osto is designed for teams that want to consolidate security and compliance work across cloud, applications, APIs, endpoints, networks and code, while also managing audit readiness, VAPT and security questionnaires in the same platform.
Osto vs Rapid7: security operations platform vs one-stop cyber platform
Rapid7: exposure, detection and response
Rapid7 brings together vulnerability and exposure management, SIEM, cloud and application security, threat intelligence, MDR services and CyberGRC. Its platform is especially relevant when security teams need visibility, prioritisation, investigation and response workflows across a larger attack surface.
Osto: security, compliance and VAPT together
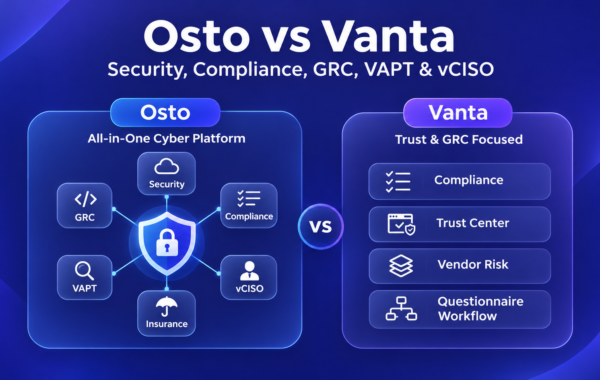
Osto brings preventive security controls, compliance automation, GRC-related workflows, security questionnaires, expert-led VAPT, vCISO support and cyber insurance access into one platform focused on startups and growing technology teams.
Osto vs Rapid7: cybersecurity, compliance automation and VAPT
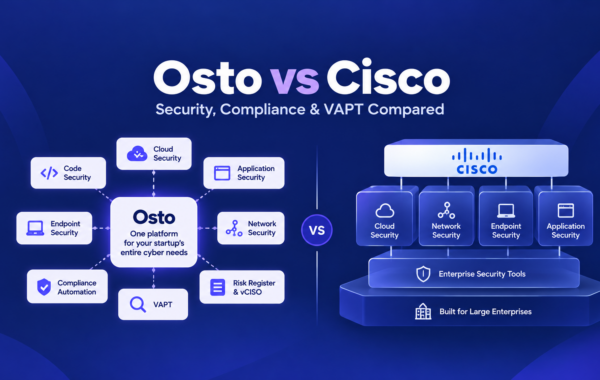
Osto’s advantage is consolidation across areas that growing teams often manage through several separate tools or providers. The platform covers:
- Cloud security: CSPM across AWS, Azure and GCP, with continuous posture monitoring and remediation guidance.
- Application and API security: web and API protection, discovery, scanning and behaviour-aware monitoring. Learn more about API security.
- Endpoint and access security: antimalware, device and application control, file access DLP, disk encryption, screen lock and ZTNA.
- Code security: SAST, SCA, SBOM and licence compliance.
- Compliance and GRC-related workflows: control mapping, evidence, monitoring, policies, questionnaires and audit-readiness workflows. See Osto’s GRC guide.
- Security services: expert-led VAPT, remediation support, retesting and vCISO support.
Rapid7 has deeper capabilities in areas such as exposure management, vulnerability prioritisation, SIEM, threat intelligence, MDR and security operations. The comparison is therefore less about which company has “more security” and more about which operating model matches your team.
Osto vs Rapid7 comparison: 7 key cybersecurity criteria
| Criteria | Osto | Rapid7 |
|---|---|---|
| What is the platform mainly designed around? | Consolidating preventive security, compliance, VAPT and ongoing security support for growing teams. | Exposure management, vulnerability management, detection, investigation, response and security operations. |
| Does it cover cloud security? | Yes. CSPM across AWS, Azure and GCP, alongside other security and compliance modules. | Yes. Rapid7 provides cloud-native application protection, cloud posture and workload capabilities within its broader platform. |
| What about application security? | Web and API protection plus web, API and mobile scanning, with security controls and testing connected to the wider platform. | Rapid7 provides application security testing, including dynamic application security testing, as part of its exposure-management portfolio. |
| How strong is vulnerability and exposure management? | Vulnerability findings appear across Osto’s security modules and VAPT workflows, with remediation guidance and retesting. | A core Rapid7 strength, with vulnerability management, attack-surface visibility, risk-based prioritisation and exposure-management workflows. |
| Does it support detection and response? | Osto supports security monitoring and platform-level protection, with SIEM forwarding available where teams need broader operations workflows. | Yes. Rapid7 offers next-generation SIEM, EDR/XDR-related capabilities, automation, threat intelligence, incident-response workflows and MDR services. |
| Can it support compliance and GRC? | Yes. Osto connects compliance automation and GRC-related workflows to the security controls and evidence managed in the platform. | Yes. Rapid7 offers CyberGRC for governance, risk and compliance alongside its broader security platform. |
| Is penetration testing available? | Yes. Expert-led VAPT is part of Osto’s broader offering, with remediation support and retesting. | Yes. Rapid7 offers penetration testing and continuous red teaming as professional and managed security services. |
Osto vs Rapid7: which cybersecurity platform fits your team?
Rapid7 may make sense when
- Exposure management and vulnerability prioritisation are major parts of your security program.
- You need SIEM, investigation and response workflows across a broad environment.
- You are evaluating MDR or other managed security operations services.
- Your security team wants deeper operational tooling around threat detection and attack-surface management.
Osto may make sense when
- You want to consolidate security, compliance automation and VAPT into fewer tools and providers.
- Your immediate requirements span cloud, applications, APIs, endpoints, network/access and code security.
- Audit readiness, security questionnaires and customer assurance are closely tied to your security work.
- You are looking for a Rapid7 alternative for startups that combines product security and compliance workflows in one platform.
Can Osto and Rapid7 work together?
Yes. These platforms do not have to be mutually exclusive. A company can use Rapid7 for exposure management, SIEM, threat intelligence or managed detection and response while using Osto for preventive controls, compliance automation, VAPT and other startup-focused security workflows. The right combination depends on your existing stack, team structure and security priorities.
Related Osto security guides
Osto vs Rapid7: common questions
What is the main difference between Osto and Rapid7?
Rapid7 is built around exposure management and security operations, with capabilities across vulnerability management, SIEM, cloud and application security, threat intelligence, MDR and GRC. Osto combines security controls with compliance automation, VAPT and security-support workflows in a platform designed around startups and growing teams.
Is Osto a Rapid7 alternative for startups?
It can be, depending on what you need. Osto is most relevant when your priority is consolidating security, compliance automation, VAPT and customer-assurance workflows. Teams primarily looking for deep exposure management, SIEM or managed detection and response may evaluate Rapid7 for those requirements.
Does Rapid7 offer cloud security?
Yes. Rapid7 offers cloud-native application protection and cloud security capabilities, including visibility, configuration assessment, vulnerability assessment, attack-path analysis and automated remediation workflows.
Does Rapid7 offer GRC?
Yes. Rapid7 offers CyberGRC for governance, risk and compliance. Osto also supports GRC-related and compliance workflows, with evidence connected to the security controls managed through the platform.
Does Rapid7 offer penetration testing?
Yes. Rapid7 offers penetration testing services and continuous red teaming. Osto also provides expert-led VAPT with remediation support and retesting as part of its broader cyber offering.
How long does SOC 2 Type II take?
A SOC 2 Type II report includes an observation period. The appropriate period is agreed with the independent CPA firm and commonly runs for several months. Total timing depends on readiness, scope, remediation work and auditor scheduling. For the underlying SOC 2 criteria and reporting resources, see the AICPA SOC 2 resources.
Bring more of your startup’s cyber program into one place
See how Osto combines security, compliance automation, VAPT and ongoing security support for growing teams.
Talk to Osto