
 Blog
The HIPAA Business Associate Agreement: What Hospitals Actually Read Before Signing
The HIPAA Business Associate Agreement is what hospitals scrutinise most before signing. What they read, what they reject,…
Blog
The HIPAA Business Associate Agreement is what hospitals scrutinise most before signing. What they read, what they reject,…
 Blog
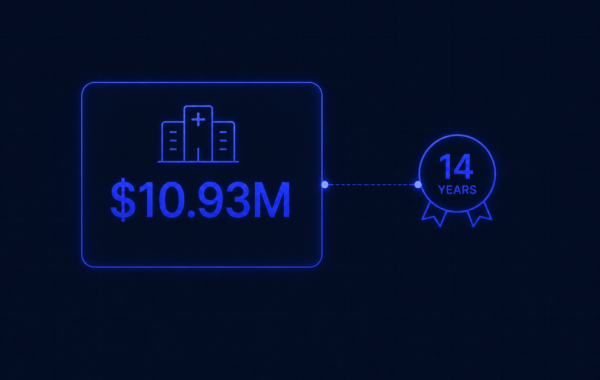
Healthcare has had the most expensive data breaches of any industry for 14 consecutive years. The average breach…
 Blog
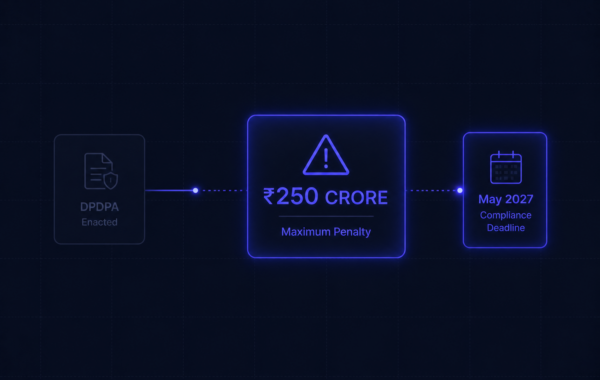
DPDPA for Indian fintechs explained. What the Rs 250 crore penalty means for your platform, the May 2027…
 Blog
The Indian fintech compliance map. RBI Master Directions, CERT-In, PCI DSS, SOC 2, DPDPA. What is mandatory, what…
 Blog
41.8% of fintech breaches don't start with you. They start with your vendors. How to manage third-party risk…
 Blog
The $5.56 million number every fintech founder ignores until it is too late. Average fintech breach cost, IBM…
 Blog
The 60-day rule for B2B SaaS founders: security infrastructure must exist before the first enterprise sales hire. Why…
 Blog
Paper compliance vs real security. Why a SOC 2 badge does not mean you are protected, and how…
 Blog
TL;DR The security questionnaire is the most common reason enterprise B2B SaaS deals stall in the final mile.…