 Blog
Blog
Security writing for fast-moving teams.
Deep dives, how-tos and security perspectives from the people building Osto.
Blog
 Blog
SOC 2 Readiness Checklist for Startups
Map your controls, close the gaps, and collect clean evidence before a CPA firm ever shows up. Osto Security Team… Blog
SOC 2 for Startups: What It Is and Why It Matters
The credential that unlocks enterprise deals. Osto Security Team 7 min read Compliance & Trust TL;DR SOC 2 is an… Blog
SOC 2 Type I vs Type II: What Enterprise Buyers Actually Check
SOC 2 Type I vs Type II explained. What enterprise buyers actually check during procurement, and which audit type your B2B SaaS… Blog
Why Your Clinical AI Demo Went Perfectly and the Deal Still Hasn’t Closed in Four Months
Why your clinical AI demo went perfectly but the deal has not closed. What hospital procurement and security review actually look like… Blog
HIPAA for Indian Healthtech Founders: What It Actually Requires and Why Your Hospital Pilot Is Blocked Without It
HIPAA for Indian healthtech founders. What it actually requires, why your US hospital pilot is blocked without it, and how to become… Blog
The HIPAA Business Associate Agreement: What Hospitals Actually Read Before Signing
The HIPAA Business Associate Agreement is what hospitals scrutinise most before signing. What they read, what they reject, and how to structure… Blog
Healthcare Has the Most Expensive Data Breaches in Any Industry. For the 14th Year in a Row.
Healthcare has had the most expensive data breaches of any industry for 14 consecutive years. The average breach now costs $7.42M. Here's…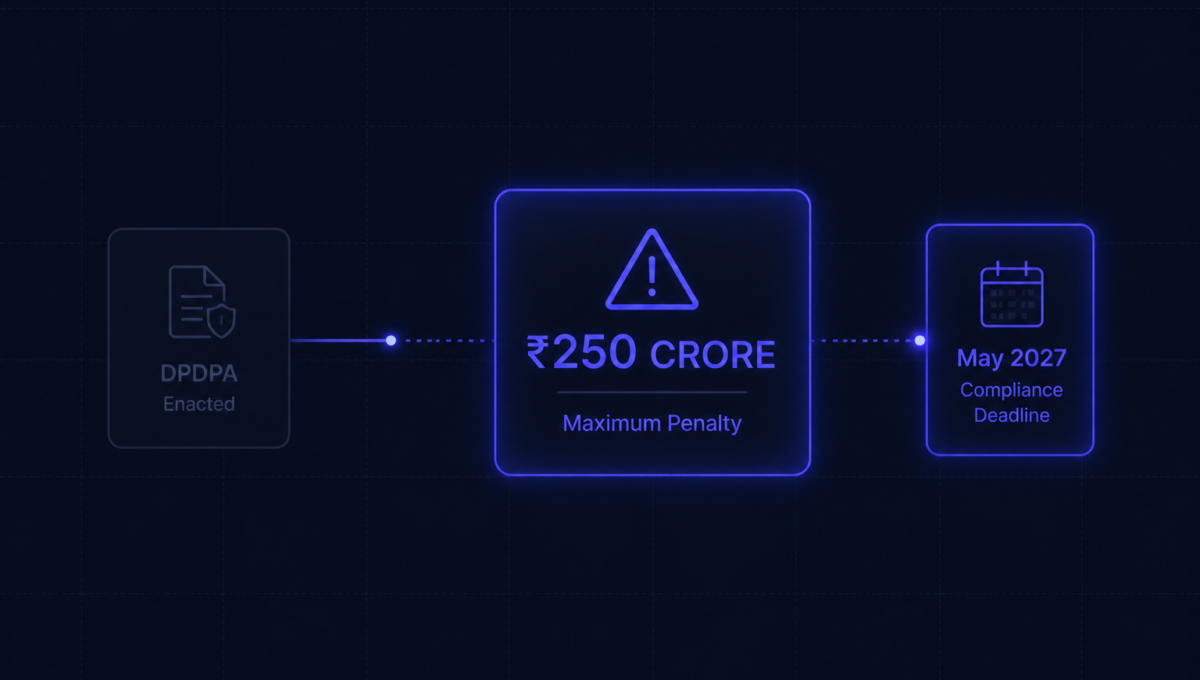 Blog
DPDPA for Fintechs: What the Rs 250 Crore Penalty Means for Your Platform (And What to Do Before May 2027)
DPDPA for Indian fintechs explained. What the Rs 250 crore penalty means for your platform, the May 2027 deadline, and the security… Blog