
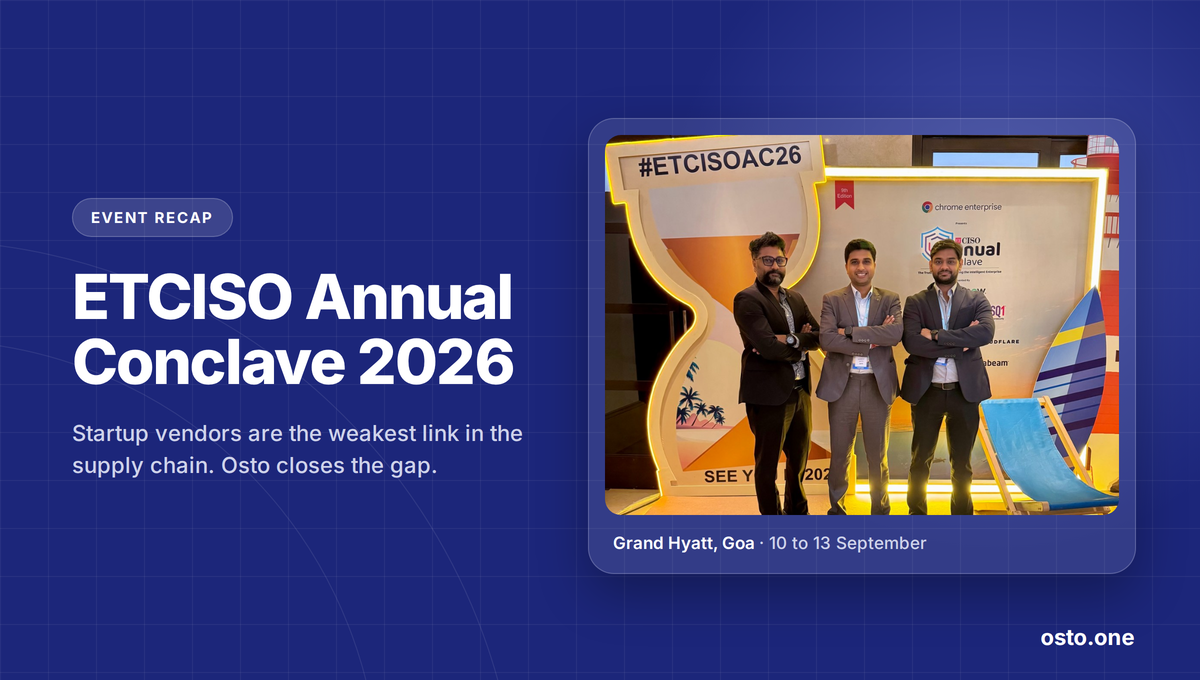
Osto joined the 9th ETCISO Annual Conclave in Goa as a partner, with one message for India’s security leaders: the startups inside your supply chain can be your most secure vendors, not your weakest.
TL;DR
The ETCISO Annual Conclave is a residential gathering where India’s CISOs spend several days together on one campus. The 9th edition ran from 10 to 13 September 2026 at Grand Hyatt, Goa. Osto was there as a partner, exhibiting and meeting security leaders to talk about the problem sitting at the top of most vendor risk registers: startups are now among the fastest-growing groups of third parties plugged into enterprise systems, and their security posture rarely matches what a CISO needs.
Most security conferences give CISOs a few hours. The ETCISO Annual Conclave gives them several days in one place, which is why the conversations there go further than anywhere else on the calendar.
What the ETCISO Annual Conclave is
The ETCISO Annual Conclave is run by ETCISO, the cybersecurity platform of The Economic Times, and is one of the most celebrated events for enterprise security leaders in India. It is residential by design. CISOs stay on the same campus for the length of the event, so the sessions, the meals and the evenings all become part of the conversation.
| Detail | ETCISO Annual Conclave 2026 |
|---|---|
| Edition | 9th |
| Dates | 10 to 13 September 2026 |
| Venue | Grand Hyatt, Goa |
| Organiser | ETCISO, The Economic Times |
| Presented by | Chrome Enterprise |
| Format | Residential. Keynotes, panel discussions, an exhibition floor and closed-door conversations |
| Who attends | CISOs and security leaders from enterprises across sectors, with technology and security vendors exhibiting alongside |
This year the agenda moved from resilience to trust. The framing was that the enterprise is now AI-enabled and dependent on a wide ecosystem of partners, so CISOs are being asked to create confidence across AI, data, identity, regulation and business continuity, not just to secure assets and respond to incidents.

Vendors play an active role at the ETCISO Annual Conclave. Security companies exhibit, speak on panels and meet CISOs and CTOs directly, which makes it one of the few rooms where the people buying security and the people building it sit at the same table for days at a time.
The problem CISOs are carrying
Enterprise AI adoption has changed who an enterprise buys from. A large and growing share of the third parties plugging into enterprise systems are startups: young companies with a sharp product, direct access to data, and an engineering team with no dedicated security hire.
That makes them the weakest link in the supply chain. Not because startups are careless, but because security maturity takes time and budget that a two-year-old company rarely has. A CISO wants every vendor to arrive with tested applications, documented controls, a data protection posture and a plan for when something goes wrong. Most startups arrive with a promise to get there.
| What a CISO asks for | What a startup vendor often has | What Osto puts in place |
|---|---|---|
| Evidence of security testing | No recent test, or an old report | Expert-led VAPT with remediation tracked to closure |
| Documented controls | Policies in draft, no audit trail | Compliance automation for SOC 2, ISO 27001 and DPDP |
| Continuous posture | Point-in-time checks before a deal | Code, cloud, endpoint and email security monitored in one dashboard |
| A financial backstop | No cyber cover | Cyber insurance readiness, with cover placed through Osto’s licensed distribution partner |
| Someone accountable | Security owned by whoever has time | A vCISO who owns the programme |
Why Osto was there
Osto works primarily with startups in regulated markets, and the companies we work with are exactly the third parties CISOs worry about. We went to the ETCISO Annual Conclave as a partner to show the other side of that relationship: how a startup vendor can arrive at the security review with the posture an enterprise expects.

Our message on the floor was simple. When the startups in your ecosystem run security, compliance and insurance readiness on one platform, you stop chasing evidence and start getting it by default. That gives a CISO more confidence in the vendors being integrated into their environment, and gives the startup a faster path through procurement.
The team on the ground
Three of us represented Osto across the conclave, exhibiting, presenting the platform and meeting security leaders through the four days.

What we are taking back
The response was overwhelmingly positive. The idea landed quickly with the leaders we met, because almost every one of them has a startup vendor they are worried about, and very few have a practical way to raise that vendor’s posture.
The takeaway
Third-party risk is increasingly startup risk. The fix is not fewer startups in the supply chain. It is startups that arrive secure, compliant and insured from day one, and that is what Osto builds for.
We look forward to being part of more rooms like this one.
For startups selling to enterprise
Pass the vendor security review the first time
Security, compliance and cyber insurance readiness in one platform, purpose-built for startups whose buyers ask hard questions.
Book a demoOne platform · One dashboard · One owner
Frequently asked questions
When and where was the ETCISO Annual Conclave 2026 held?
The 9th edition was held from 10 to 13 September 2026 at Grand Hyatt, Goa.
Who organises the ETCISO Annual Conclave?
ETCISO, the cybersecurity platform of The Economic Times. The 2026 edition was presented by Chrome Enterprise.
Why are startups a supply chain risk for enterprises?
Startups often have direct access to enterprise data and systems, but rarely have a dedicated security team, a recent security test or documented controls. That gap is what makes them a common weak point in third-party risk.
Is Osto an insurer?
No. Osto helps startups get ready for cyber insurance by putting the right controls in place. Cover is placed through Osto’s licensed insurance distribution partner, and underwriting and claims decisions rest with the insurer.
Osto joined the 9th ETCISO Annual Conclave in Goa as a partner, with one message for India’s security leaders: the startups inside your supply chain can be your most secure vendors, not your weakest.
TL;DR
The ETCISO Annual Conclave is a residential gathering where India’s CISOs spend several days together on one campus. The 9th edition ran from 10 to 13 September 2026 at Grand Hyatt, Goa. Osto was there as a partner, exhibiting and meeting security leaders to talk about the problem sitting at the top of most vendor risk registers: startups are now among the fastest-growing groups of third parties plugged into enterprise systems, and their security posture rarely matches what a CISO needs.
Most security conferences give CISOs a few hours. The ETCISO Annual Conclave gives them several days in one place, which is why the conversations there go further than anywhere else on the calendar.
What the ETCISO Annual Conclave is
The ETCISO Annual Conclave is run by ETCISO, the cybersecurity platform of The Economic Times, and is one of the most celebrated events for enterprise security leaders in India. It is residential by design. CISOs stay on the same campus for the length of the event, so the sessions, the meals and the evenings all become part of the conversation.
| Detail | ETCISO Annual Conclave 2026 |
|---|---|
| Edition | 9th |
| Dates | 10 to 13 September 2026 |
| Venue | Grand Hyatt, Goa |
| Organiser | ETCISO, The Economic Times |
| Presented by | Chrome Enterprise |
| Format | Residential. Keynotes, panel discussions, an exhibition floor and closed-door conversations |
| Who attends | CISOs and security leaders from enterprises across sectors, with technology and security vendors exhibiting alongside |
This year the agenda moved from resilience to trust. The framing was that the enterprise is now AI-enabled and dependent on a wide ecosystem of partners, so CISOs are being asked to create confidence across AI, data, identity, regulation and business continuity, not just to secure assets and respond to incidents.
Vendors play an active role at the ETCISO Annual Conclave. Security companies exhibit, speak on panels and meet CISOs and CTOs directly, which makes it one of the few rooms where the people buying security and the people building it sit at the same table for days at a time.
The problem CISOs are carrying
Enterprise AI adoption has changed who an enterprise buys from. A large and growing share of the third parties plugging into enterprise systems are startups: young companies with a sharp product, direct access to data, and an engineering team with no dedicated security hire.
That makes them the weakest link in the supply chain. Not because startups are careless, but because security maturity takes time and budget that a two-year-old company rarely has. A CISO wants every vendor to arrive with tested applications, documented controls, a data protection posture and a plan for when something goes wrong. Most startups arrive with a promise to get there.
| What a CISO asks for | What a startup vendor often has | What Osto puts in place |
|---|---|---|
| Evidence of security testing | No recent test, or an old report | Expert-led VAPT with remediation tracked to closure |
| Documented controls | Policies in draft, no audit trail | Compliance automation for SOC 2, ISO 27001 and DPDP |
| Continuous posture | Point-in-time checks before a deal | Code, cloud, endpoint and email security monitored in one dashboard |
| A financial backstop | No cyber cover | Cyber insurance readiness, with cover placed through Osto’s licensed distribution partner |
| Someone accountable | Security owned by whoever has time | A vCISO who owns the programme |
Why Osto was there
Osto works primarily with startups in regulated markets, and the companies we work with are exactly the third parties CISOs worry about. We went to the ETCISO Annual Conclave as a partner to show the other side of that relationship: how a startup vendor can arrive at the security review with the posture an enterprise expects.
Our message on the floor was simple. When the startups in your ecosystem run security, compliance and insurance readiness on one platform, you stop chasing evidence and start getting it by default. That gives a CISO more confidence in the vendors being integrated into their environment, and gives the startup a faster path through procurement.
The team on the ground
Three of us represented Osto across the conclave, exhibiting, presenting the platform and meeting security leaders through the four days.
What we are taking back
The response was overwhelmingly positive. The idea landed quickly with the leaders we met, because almost every one of them has a startup vendor they are worried about, and very few have a practical way to raise that vendor’s posture.
The takeaway
Third-party risk is increasingly startup risk. The fix is not fewer startups in the supply chain. It is startups that arrive secure, compliant and insured from day one, and that is what Osto builds for.
We look forward to being part of more rooms like this one.
For startups selling to enterprise
Pass the vendor security review the first time
Security, compliance and cyber insurance readiness in one platform, purpose-built for startups whose buyers ask hard questions.
Book a demoOne platform · One dashboard · One owner
Frequently asked questions
When and where was the ETCISO Annual Conclave 2026 held?
The 9th edition was held from 10 to 13 September 2026 at Grand Hyatt, Goa.
Who organises the ETCISO Annual Conclave?
ETCISO, the cybersecurity platform of The Economic Times. The 2026 edition was presented by Chrome Enterprise.
Why are startups a supply chain risk for enterprises?
Startups often have direct access to enterprise data and systems, but rarely have a dedicated security team, a recent security test or documented controls. That gap is what makes them a common weak point in third-party risk.
Is Osto an insurer?
No. Osto helps startups get ready for cyber insurance by putting the right controls in place. Cover is placed through Osto’s licensed insurance distribution partner, and underwriting and claims decisions rest with the insurer.